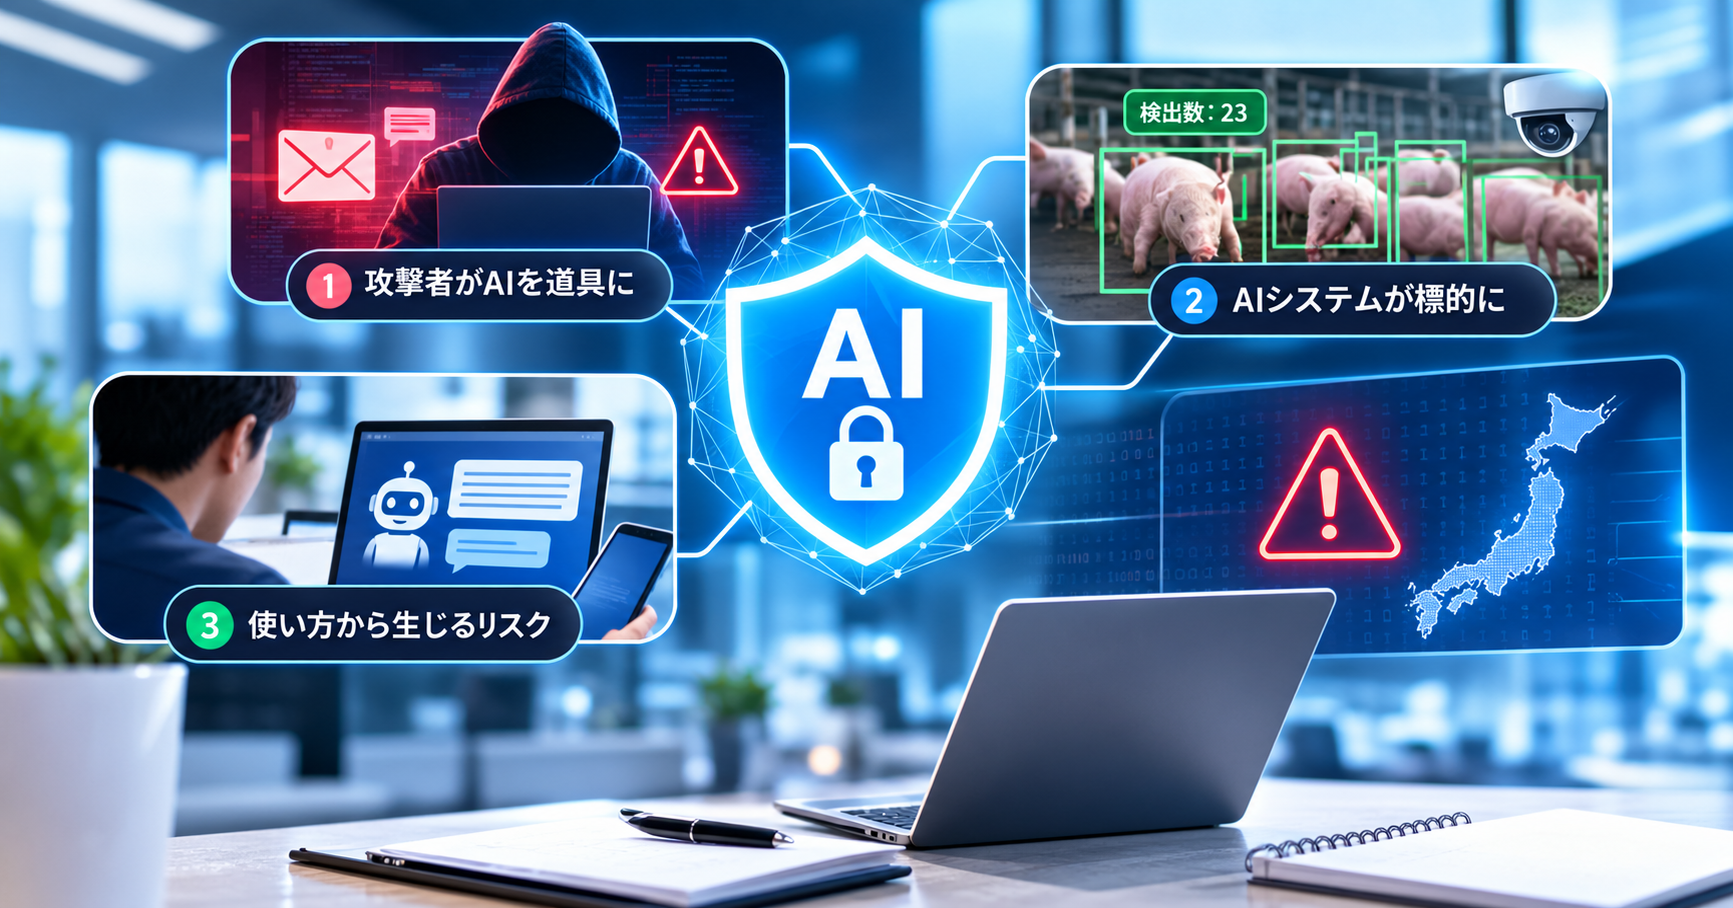
Summary: AI-driven cyberattacks (AIサイバー攻撃) fall into 3 groups. Attackers use AI as a tool, a company's own AI systems are attacked, or the risk comes from how the company uses AI. Most are old techniques that now run faster and cheaper. Basic measures therefore still work, but they must be done faster and extended to cover AI.
Part 1 of 6 in the series "AI-Driven Cyberattacks in Japan". This post is the overall map. The next 5 posts go deeper into each group.
Contents
- Why do Japanese companies have to talk about AI-driven cyberattacks in 2026?
- What is an AI-driven cyberattack?
- What groups do AI-driven cyberattacks fall into?
- Which incidents have actually happened in Japan?
- Can AI already attack by itself, without humans?
- What should your company do first?
- What can this series not replace?
1. Why do Japanese companies have to talk about AI-driven cyberattacks in 2026?
In 2026, AI-related cybersecurity risk entered Japan's official threat list for the first time. The Information-technology Promotion Agency (IPA, 独立行政法人情報処理推進機構) published "10 Major Security Threats 2026" (情報セキュリティ10大脅威 2026) on January 29, 2026. In it, "cyber risks surrounding the use of AI" (「AIの利用をめぐるサイバーリスク」) ranks 3rd in the organizations category. Ransomware ranks 1st. Attacks through the supply chain and contractors rank 2nd.
This list is not a forecast. IPA selects from incidents with a large social impact in 2025, by vote of about 250 experts and practitioners. IPA also notes that the ranking does not indicate the level of danger.
Police figures show the general baseline is getting worse too. The National Police Agency (警察庁) report for the first half of 2026 records 123 reported ransomware cases in Japan. That is the highest half-year figure since statistics began. Small and medium-sized companies make up about 60% of the victims. Phishing reports came to about 730,000 (a figure from the Council of Anti-Phishing Japan (フィッシング対策協議会), cited by the National Police Agency).
In May 2026, the Japanese government responded across ministries. 14 government bodies jointly issued a package of measures called "Project YATA-Shield" on May 18, 2026. Four days later, the Financial Services Agency (金融庁) and the Bank of Japan (日本銀行) sent a 9-item request to financial institutions.
2. What is an AI-driven cyberattack?
"AI-driven cyberattack" is an umbrella term for the cybersecurity risks that arise when AI takes part in an attack. AI can be the tool, the target or the gap. In Japanese it is usually called AIサイバー攻撃 or AIを悪用したサイバー攻撃.
This definition is broader than the common reading, "hackers using AI". IPA describes the 3rd-ranked threat as covering three things. AI is abused to make attacks easier and more sophisticated. Information leaks when people use AI without understanding it well enough. Incidents happen when people trust AI output without checking it.
One IPA observation helps companies avoid overreacting. In its accompanying explanatory document, IPA sets aside indirect prompt injection (planting instructions in data the AI reads). Apart from that, it writes, most cases are older attacks that AI has semi-automated and sped up. Traditional cybersecurity measures therefore remain effective.
| Common assumption | What public documents show |
|---|---|
| A completely new kind of attack | Mostly phishing, malware and vulnerability exploitation, running faster and cheaper |
| Only large companies are hit | Attack costs have fallen, so small companies are also in range |
| A job for the IT department | The Financial Services Agency asks the management of financial institutions to treat it as a business issue |
| Only about attacks from outside | Also covers leaks caused by employees using AI outside company control |
3. What groups do AI-driven cyberattacks fall into?
AI-driven cyberattacks can be divided into 3 groups by the role AI plays. This series uses a division based on IPA's description, because each group needs a different part of the company to handle it.
| Group | Role of AI | Common forms | Who in the company owns it | Deep-dive post |
|---|---|---|---|---|
| 1A | Tool, aimed at people | Phishing, BEC (business email compromise), deepfakes, fake-CEO fraud (ニセ社長詐欺) | Accounting, general affairs, management | Part 2 |
| 1B | Tool, aimed at systems | AI-written malware, fast vulnerability exploitation, AI agents attacking autonomously | IT, the development and maintenance vendor | Part 3 |
| 2 | Target | Prompt injection, data poisoning, AI agents with overly broad permissions | The team building the AI system | Part 4 |
| 3 | Operational gap | Shadow AI, trusting AI output without checking, vulnerabilities in AI-generated code | Every department, the development team | Part 5 |
Group 1: attackers use AI as a tool. This group has the most real incidents. AI writes scam emails in natural Japanese, creates fake faces and voices, and writes and modifies malware. According to IPA, AI helps attackers get past the language barrier. The "Japanese is hard" advantage of Japanese companies is shrinking as a result.
Group 2: the company's AI systems are attacked. When a company puts a chatbot or an AI agent into its operations, that system becomes a new attack surface. The example IPA gives is EchoLeak, a Microsoft 365 Copilot vulnerability disclosed in June 2025. A prompt hidden in an email could make the AI send internal data outside without any action by the user. This vulnerability has been patched.
Group 3: risks from how the company itself uses AI. There is no attacker here. Employees paste internal documents into AI services the company does not manage (shadow AI), or use AI output without checking it. IPA cites a 2025 survey by LayerX: 77% of users paste data into generative AI. Of those, 82% use accounts the organization does not manage.
4. Which incidents have actually happened in Japan?
In Japan, police have already made and announced arrests in cases where AI was used to attack. Many of the suspects are young people without deep expertise. The table below lists only incidents found in National Police Agency reports and IPA documents.
| When | What happened | AI was used to | Source |
|---|---|---|---|
| January 2025 | A 17-year-old student sent about 7.24 million unauthorized commands to the app server of an internet cafe chain, exposing member information | Write the attack program | National Police Agency, 2025 annual report |
| February 2025 | 3 junior high and high school students were arrested for signing mobile phone contracts with illegally obtained IDs and passwords | Help write an automation program | IPA, citing Nikkei |
| November 2025 | A 15-year-old student caused about 46,800 accounts of a video service to be cancelled against the users' will | Modify a self-written attack program | National Police Agency, first half of 2026 |
| February 2026 | A 19-year-old male employee assembled AI-generated source code into ransomware and was arrested in June 2026 | Generate source code | National Police Agency, first half of 2026 |
| October 2024 to May 2025 | A fraud group impersonated police officers over video calls | Create fake faces | National Police Agency, first half of 2026 |
What these cases share is a lower skill barrier. The National Police Agency assesses that generative AI makes cyberattacks easier to carry out for people without advanced technical skills. For companies, the result is more attacks overall, including on firms that were previously "not worth the effort".
Fraud aimed at company money is also rising fast. From January to June 2026, the National Police Agency recorded 127 cases of fake-CEO fraud (impersonating a company president by email and social media groups). Losses came to about ¥3.88 billion. The report does not say these cases used AI. But this is exactly the kind of scheme that AI makes harder to spot.
5. Can AI already attack by itself, without humans?
AI has already carried out most of an attack campaign by itself and, in one disclosed incident, an entire intrusion. Public evaluations have not yet concluded whether AI can get past systems that are well defended and monitored. The three documents below show both the capability and the limits.
- Anthropic (November 13, 2025). A group assessed to be state-sponsored abused the Claude Code tool to target about 30 organizations, and succeeded against a small number. AI carried out 80 to 90% of the campaign. Humans stepped in at only about 4 to 6 decision points. Limit: the AI sometimes "made up" login credentials that did not exist.
- UK AI Security Institute (April 13, 2026). Claude Mythos Preview was the first model to complete a simulated 32-step attack chain, in 3 out of 10 attempts. The institute states clearly that the test environment had no defenders. It therefore cannot yet say the model could attack well-defended systems.
- Hugging Face (July 16, 2026). The company disclosed unauthorized access to some internal datasets and credentials. According to Hugging Face, the intrusion was carried out end to end by an autonomous AI agent system.
The Financial Services Agency also cites the UK institute's evaluation in its document of May 22, 2026. It then concludes that carrying out basic measures faster and more reliably remains what matters. In other words, Japan's regulators are not asking companies to buy something entirely new. They are asking for the old work at a new speed.
Speed is what has changed most clearly. CrowdStrike's "2026 Global Threat Report" puts the average time from intrusion to the attacker spreading to another machine at 29 minutes in 2025. That is 65% faster than in 2024.
6. What should your company do first?
Start by identifying which risk group your company is in, because each group has a different owner and different measures. The four steps below need no new budget.
- Check your money transfer process. Every request by email, chat or call to transfer money or change a payee account must be verified through a second channel. IPA recommends rules that require several people to check at the approval stage. Details in Part 2.
- List your critical systems and who patches them. For each system: who patches it, how fast, and whether the maintenance contract covers this work. Details in Part 3.
- List the AI systems you run and their permissions. Which data can the AI read, and which actions can it take by itself? Details in Part 4.
- Define which AI services may be used and which data may be entered. A total ban usually pushes employees into using AI in secret. Details in Part 5.
Part 6 gathers these tasks into a 30-day checklist, with a set of questions to send to your software development and maintenance vendor.
For its own part, VAON develops software and AI systems, so it is directly responsible for steps 2 to 4. The Project YATA-Shield package calls on software vendors to find and handle vulnerabilities early across the whole development lifecycle. This follows the secure by design (セキュア・バイ・デザイン) principle. At VAON, every project keeps review and test records, and clients can view those records. This is the minimum a development vendor needs in order to answer the question "who checked this code?".
7. What can this series not replace?
This series cannot replace an assessment by security specialists, and it is not legal advice. VAON is not a security company. VAON does not provide 24-hour monitoring (SOC), incident response or penetration testing.
In three cases, you should go to a specialist provider instead of stopping at reading:
- Your company suspects it has already been breached. In that case, contact an incident response provider and the police.
- Your company is in a sector with its own rules, such as finance, healthcare or critical infrastructure. From October 1, 2026, designated critical infrastructure operators also have an incident reporting obligation under the Cyber Response Capability Strengthening Act (サイバー対処能力強化法).
- Your company needs continuous monitoring outside working hours.
The situation is also changing fast. IPA writes that the current state may change within a few months. The figures in this series were checked against the original sources on October 10, 2026.
Are you building or running an AI system and want to know which risk group it falls into? VAON can review with you what data the AI system reads, what it is allowed to do and who has checked it. Book a free consultation
Posts in this series
- AI-Driven Cyberattacks in Japan: What They Are, 3 Risk Groups, and What to Do First (this post)
- AI phishing and deepfakes: why the defense has to be process
- AI-written malware and faster vulnerability exploitation
- Prompt injection and attacks on RAG systems and AI agents
- Shadow AI and AI-generated code: risks from how you use AI
- A 30-day checklist and the questions to send your vendor
References (checked Oct 10, 2026)
- IPA, 情報セキュリティ10大脅威 2026 and the explanatory document for organizations: https://www.ipa.go.jp/security/10threats/10threats2026.html
- National Police Agency (警察庁), 令和8年上半期におけるサイバー空間をめぐる脅威の情勢等について (September 2026): https://www.npa.go.jp/publications/statistics/cybersecurity/data/R8kami/R08_kami_cyber_jousei.pdf
- National Cybersecurity Office (国家サイバー統括室) and 13 other bodies, AI性能の高度化を踏まえたサイバーセキュリティ対策の強化について ~Project YATA-Shield~ (May 18, 2026): https://www.cyber.go.jp/pdf/press/20260518_AI_CS_Package.pdf
- Anthropic, Disrupting the first reported AI-orchestrated cyber espionage campaign (November 13, 2025): https://www.anthropic.com/news/disrupting-AI-espionage
- UK AI Security Institute, Our evaluation of Claude Mythos Preview's cyber capabilities (April 13, 2026): https://www.aisi.gov.uk/blog/our-evaluation-of-claude-mythos-previews-cyber-capabilities